An unauthorised application can now directly affect the compliance state of a Windows device. The software compliance policy in Microsoft Intune lets you link this detection to Conditional Access, provided you use the right identifier and validate the whole chain on a pilot group.
Compliance blocks access, not execution
As of 21 November 2026, the software compliance policy announced by Microsoft remains in public preview. It can mark a Windows device as non-compliant when a prohibited application is detected on it.
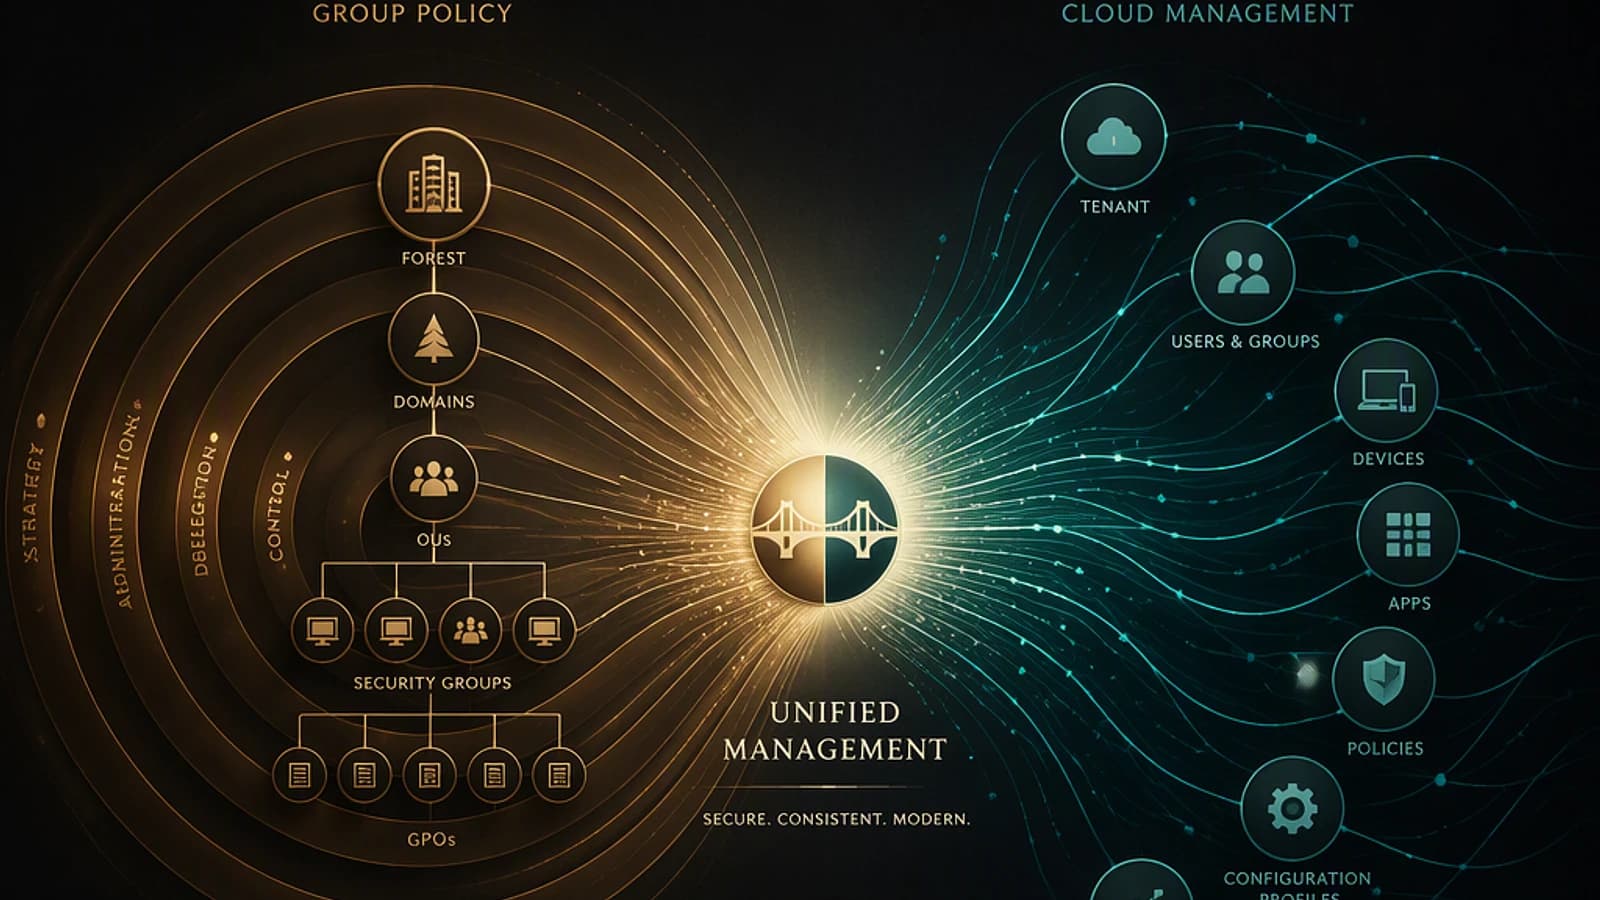
This policy does not directly block the software from launching. It changes the device's compliance state. A Microsoft Entra ID (formerly Azure AD) Conditional Access policy can then deny access to the targeted resources if it requires a compliant device.
The control chain therefore relies on four distinct elements:
- reliable identification of the application;
- the Intune software compliance policy;
- its assignment to the right group of users or devices;
- a Conditional Access policy requiring a compliant device.
Without Conditional Access, no access is blocked
The Intune policy can mark the device as non-compliant without having any effect on sign-ins. Blocking depends on a correctly targeted Conditional Access policy that requires a compliant device.
This separation avoids a common confusion. Compliance is a trust signal for access to resources. It does not replace an execution control policy.
The MSI identifier determines how reliable the control is
The policy does not evaluate an application from its display name, the name of its agent or a free-form string. The Microsoft guide on governing local AI agents specifies the supported identifiers:
- the MSI product code for a Win32 application distributed in Windows Installer (MSI) format;
- the package full name for an application from the Microsoft Store.
An application that relies on several host applications may require several entries. A single reference therefore does not necessarily cover all of its components.
During the preview, editor extensions, npm packages and standalone executables cannot be selected. These limits must be checked against the actual way the application is installed before choosing the native policy.
The Intune application inventory helps you find the expected value. For Win32 and Microsoft Store applications present on Windows 10 or Windows 11 devices enrolled in Intune and joined to Microsoft Entra ID, the attribute to look at is Platform-specific app ID.
This inventory requires a configuration profile specifying which properties to collect. An application missing from the inventory therefore does not immediately prove it is absent from the device: first confirm that the expected collection is configured.
Prepare the pilot
- Use a test Windows device enrolled in Microsoft Intune and joined to Microsoft Entra ID
- Configure the necessary properties in the application inventory profile
- Note the Platform-specific app ID value of the prohibited application
- Check whether the application uses an MSI product code or a Store package full name
- Create a limited pilot group to reduce the impact of an identifier or assignment error
- Confirm that a Conditional Access policy requires a compliant device for the tested resource
- Check in the tenant that the preview feature is available and which licences apply
If the test device is not yet managed, the IAMinerva guide on enrolling and configuring Windows 11 with Intune helps prepare this foundation before the compliance test.
Deploy the policy to a pilot group
Microsoft recommends starting with a small group of Windows devices. This approach limits the consequences of an incorrect identifier and lets you verify detection, compliance and access denial separately.
Collect the application identifier
Use the Intune application inventory and note the Platform-specific app ID attribute. For the MSI scenario, keep the exact product code shown in the inventory.
Create the software compliance policy
Create a compliance policy, then add the MSI product code as restricted software. Do not replace this identifier with the application's commercial name.
Limit the assignment to the pilot
Assign the policy to a restricted group of users or devices. The test Windows device must belong to the chosen scope.
Link compliance to Conditional Access
Check that a Conditional Access policy covers the user, the resource and the test conditions. It must require a compliant device for non-compliance to result in access denial.
Establish a baseline state
Before installing the prohibited application, check the device's state and attempt to access the targeted resource. This baseline will let you distinguish the effect of the new policy from a problem that already exists.
The Microsoft Learn documentation also explains how to create and assign a compliance policy in Intune. It should remain the reference for the screens and options available in your tenant.
Verify non-compliance on the Windows device
Consider a pilot configuration. The security team has a dedicated Windows device, an MSI application identified as prohibited and a corporate resource covered by Conditional Access.
The application must not be present during the baseline state. The device must also satisfy the other applicable rules. Otherwise, it would be impossible to clearly attribute the non-compliance to the tested software.
Next, install the prohibited MSI application on the device, then launch it to reproduce the case of active software. After compliance is re-evaluated, the check should show that the device is no longer compliant because of the restricted software.
Validation must cover the whole chain, not just the state displayed in Intune:
- the application appears with the expected MSI product code;
- the device does receive the software compliance policy;
- the device switches to non-compliant after detection;
- a new attempt to access the targeted resource is denied by Conditional Access.
Keep these four pieces of evidence in the test file. If access remains allowed while the device is non-compliant, first examine the targeting of the Conditional Access policy and the requirement for a compliant device.
No precise detection or return-to-compliance delay is provided in the available material. These delays should therefore be measured during the pilot rather than built in as assumptions in a production procedure.
Choose between native compliance, script and App Control
The right solution depends on the desired outcome. A compliance control answers the question "can this device access resources?". An execution control answers the question "can this application start?".
| Approach | Main effect | Suitable case | Structural limitation |
|---|---|---|---|
| Intune software compliance | Marks the device as non-compliant and feeds Conditional Access | Supported Win32 MSI applications and Microsoft Store packages | Public preview and no direct blocking of execution |
| Custom compliance | Runs a local script and evaluates a JSON rules file | Standalone executables and cases not covered by the native policy | Script and rules to maintain |
| App Control for Business | Controls application execution | Preventing a piece of software from launching | Different objective from access compliance |
Before the native policy, custom compliance relied on a locally executed PowerShell script and a JSON (JavaScript Object Notation) rules file. Peter van der Woude describes this method, which remains relevant for standalone executables and other formats not covered by the preview.
To genuinely prevent an application from launching, a Microsoft support agent recommends App Control for Business in Intune. Compliance flags the deviation and can close access to resources; App Control acts on execution itself.
These approaches can be complementary. An organisation can control execution for clearly prohibited applications, then use compliance and Conditional Access to reduce the exposure of a device that no longer complies with the policy. The IAMinerva guide on blocking unauthorised software installations extends this thinking on the prevention side.
Mistakes that skew the pilot
The first mistake is entering an application name instead of the MSI product code or the Store package full name. The rule may then look correctly configured without identifying the expected software.
The second is confusing inventory with a security measure. The inventory provides the identifier and visibility. It does not by itself mark the device as non-compliant and does not block any access.
The third is testing with an application outside the preview's scope. A standalone executable, an editor extension or an npm package requires a different approach, notably custom compliance when the case can be evaluated locally.
The fourth is widening the assignment before Conditional Access has been validated. A targeting error can produce either no blocking or a wider impact than expected. The pilot group should stay limited until the four pieces of evidence have been validated.
Finally, the preview status must feature in the architecture decision. The policy should not be presented as a generally available feature until Microsoft announces that change.
Frequently asked questions
Does the Intune policy prevent the application from starting?
No. It marks the device as non-compliant when restricted software is detected. To control execution, you need to evaluate App Control for Business rather than relying on compliance alone.
Which identifiers should be used?
Use the MSI product code for a Win32 application in MSI format, or the package full name for a Microsoft Store application. The Platform-specific app ID attribute in the Intune inventory lets you find this value.
Are standalone executables supported?
Not in the preview described as of 21 November 2026. Custom compliance with a PowerShell script and a JSON rules file remains an option for cases the native policy does not cover.
Is a specific licence required?
The material provided does not specify the exact edition required for this preview. Check that it is present in the tenant and review the licence conditions before the pilot; the IAMinerva guide on making use of the Microsoft Intune licences you already own helps frame this inventory.
Can the policy be assigned to users or to devices?
Yes. The procedure published by Microsoft provides for assignment to a group of devices or users. For a first test, a restricted group makes it easier to analyse the device state and the access result.
Launch the pilot without exposing production
Start with a single MSI application whose product code has been confirmed in the inventory. Use a dedicated Windows device and a test resource already covered by a compliant-device requirement.
Decisions before deployment
- Confirm that the application format is supported by the preview
- Document the MSI product code or the Store package full name
- Define the pilot group and the resource used for the access test
- Check the device's compliant state before installing the software
- Install and launch the prohibited application, then check for non-compliance
- Test the access denial produced by Microsoft Entra ID
- Measure the observed delays before any extension of the scope
- Choose custom compliance or App Control if the need goes beyond native detection
If your priority is to block execution, start with App Control for Business. If the goal is to remove access to resources when prohibited software is detected, pilot software compliance together with Conditional Access.
Further reading
- Guide to governing local AI agents with Intune — the accepted identifiers, the preview's limits and the chain with Conditional Access.
- What's new in Intune at Ignite — the official announcement of the software compliance policy in public preview.
- Verifying installed applications as part of Windows compliance — the PowerShell script and JSON file alternative for formats not covered.
- Create a compliance policy in Intune — the Microsoft Learn documentation for creating and assigning a Windows policy.